Arista says the accelerating threat landscape requires product security to be treated as a first principle rather than an afterthought. Its response highlights the growing role of AI in defending network products and operations when threats move faster than traditional manual processes.
The cybersecurity incident known as “FortiBleed” involves a large-scale compromise campaign targeting Fortinet FortiGate firewalls and VPN gateways. Estimates suggest between 30,000 and 75,000+ devices may have been affected globally. The attack impacted organizations across government, telecom, healthcare, finance, and technology sectors in more than 190 countries.
Security teams managing Cisco infrastructure have yet another reason to stay on high alert. The networking giant has disclosed a newly discovered vulnerability that is already being exploited by attackers, despite the absence of an official security patch. The flaw affects Cisco Catalyst SD-WAN Manager and adds to a growing list of security incidents targeting enterprise networking platforms in recent months.
A few days ago, a fascinating — and honestly terrifying — story emerged from Luxembourg. According to investigations reported by The Record, a previously unknown vulnerability affecting Huawei enterprise routers allegedly caused a nationwide telecom outage that disrupted mobile networks, landlines, Internet access, and even emergency communications for more than three hours. Let that sink in for a second. Not a ransomware attack. Not a datacenter fire. Not a massive DDoS. A router vulnerability. More specifically, specially crafted network traffic reportedly triggered Huawei devices into continuous reboot loops, effectively collapsing critical telecom infrastructure across the country. And the most concerning part? Almost a year later: - no public CVE exists, - no public advisory was released, - no clear disclosure process happened, - and operators worldwide still have very limited visibility into whether similar infrastructure remains exposed. This incident should be a wake-up call for the entire industry.
Servers get patched. Workstations get patched. But firmware on your switches, routers, firewalls, and access points? That's the blind spot that attackers know about — and most security teams don't. ConnectMyAssets is the only platform that gives network teams real firmware-based vulnerability tracking — including End-of-Life detection — across their entire network infrastructure.
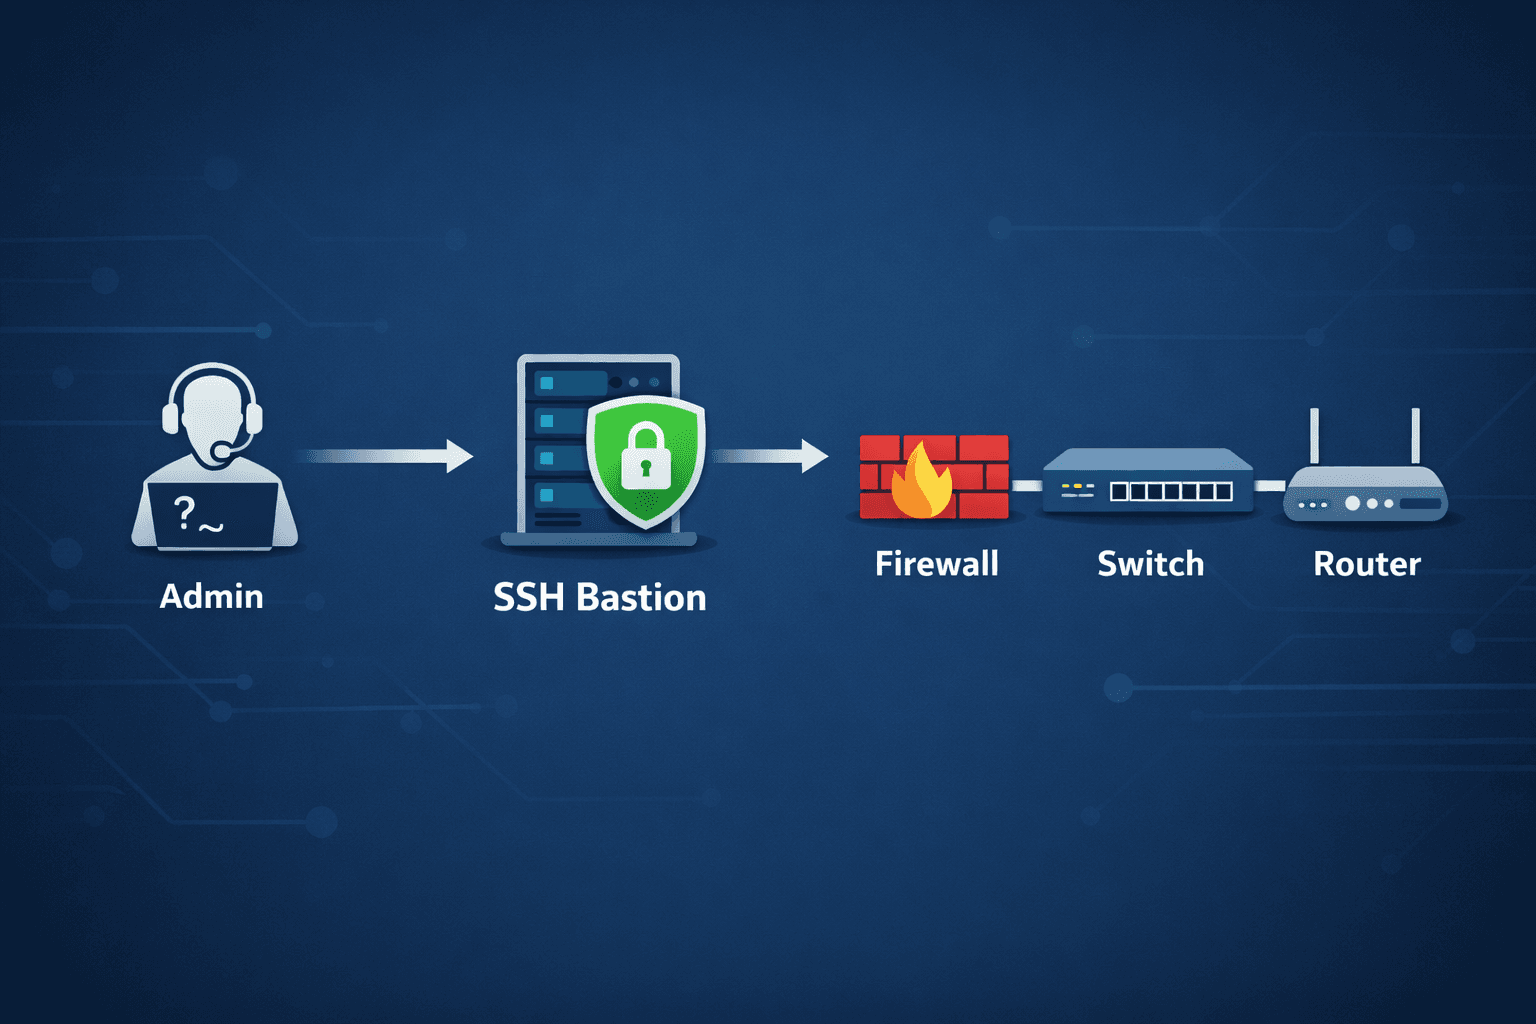
Managing network infrastructure securely is a critical responsibility for IT and network teams. Firewalls, routers, switches, and other infrastructure devices are the backbone of an organization's connectivity, and unauthorized access to these systems can lead to serious security incidents. One effective approach to strengthen security and control administrative access is the use of an SSH bastion host.
In 2025, cybersecurity giant F5 Inc. confirmed that it fell victim to a highly sophisticated, nation-state–level cyberattack. The attack, described as one of the most significant in the company’s history, exposed critical internal assets and triggered an international cybersecurity response.
A critical vulnerability (CVE-2025-20352) in the SNMP subsystem of Cisco IOS and IOS-XE is being actively exploited by threat actors. This flaw enables remote code execution or Denial of Service through a single crafted SNMP packet. With over 2 million Cisco devices exposed online, the attack surface is massive — and the urgency to patch is immediate.