From Passive Transport to Active Defense
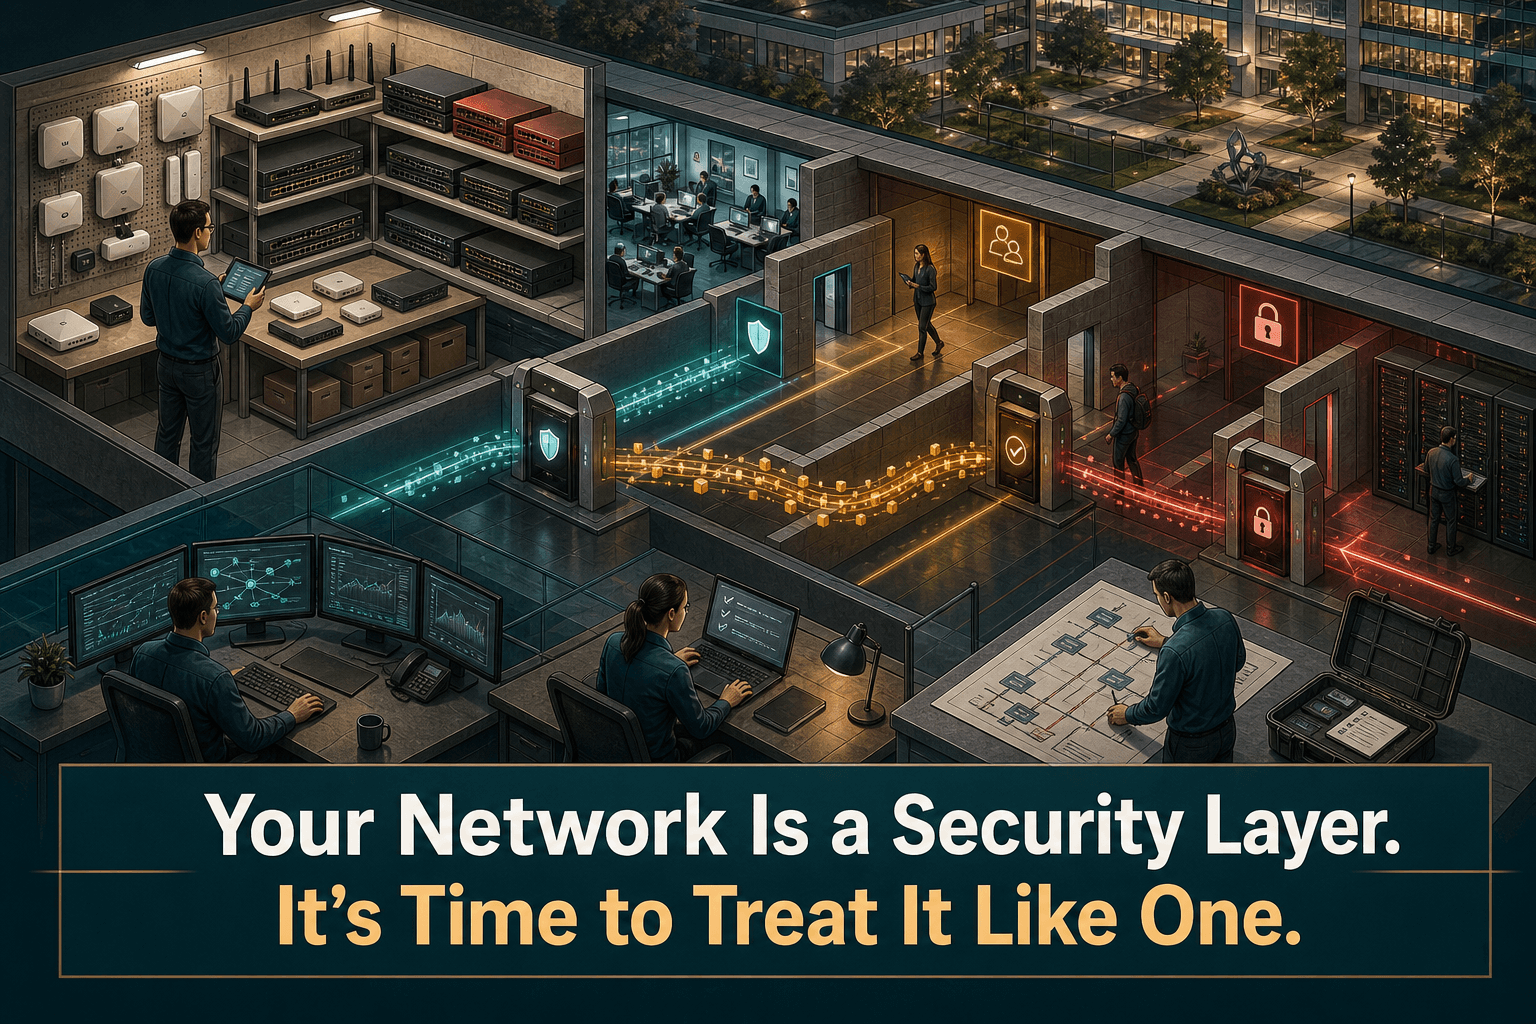
The network connects users, applications, infrastructure, and data. That position also gives it an important security role: it can help define which systems should communicate, constrain unnecessary paths, and provide the operational context needed to detect and address risk.
In its article, Cisco describes a shift from passive to active security built around three design pillars: unifying infrastructure, protecting flows, and assuring operations. The useful question for infrastructure teams is how to translate that model into controls they can operate consistently across a multi-vendor estate.
Treating the network as a security layer is not a single product decision. It is an operating model connecting asset knowledge, policy, configuration, and evidence.
Start With the Outcomes
Before changing architecture or policy, define the results the network should support. Practical priorities include:
Knowing which network assets exist, where they are, and what role they perform.
Restricting communication paths according to operational need.
Protecting traffic as it crosses security and trust boundaries.
Keeping configurations controlled, recoverable, and aligned with policy.
Identifying asset-level vulnerabilities and end-of-life exposure.
Producing evidence that security controls are reviewed and maintained.
These outcomes turn a broad security principle into work that can be assigned, measured, and repeated.
Pillar 1: Unify Infrastructure Through Inventory and Context
A unified infrastructure starts with a reliable inventory. If routers, switches, firewalls, wireless equipment, and other assets are recorded in separate spreadsheets or vendor-specific views, teams cannot easily see dependencies or apply consistent controls.
A useful inventory should connect each asset with operational context such as ownership, location, network relationships, configuration history, lifecycle status, and known vulnerability exposure. The objective is not merely to count devices. It is to understand which assets support critical paths and which gaps could weaken the security model.
Actionable controls
Establish one authoritative record for network assets across vendors.
Assign an owner, role, and location to each asset.
Record configuration history and lifecycle status alongside the asset.
Review unknown, unmanaged, or obsolete equipment as explicit risks.
Use topology and dependencies to prioritize remediation around important services.
Pillar 2: Protect Flows With Segmentation and Policy
Flow protection begins with understanding which communications are necessary. Segmentation can then reduce unnecessary reachability between users, systems, sites, and services. Firewall policy provides another control point for permitted and denied flows.
This is not a one-time design exercise. Business requirements change, applications move, and temporary exceptions can become permanent unless they are reviewed. Teams therefore need a lifecycle for network policy: define, implement, validate, document, and revisit.
Actionable controls
Group assets and services according to function and sensitivity.
Document required communication paths before defining restrictions.
Remove rules and paths that no longer have a justified purpose.
Review firewall changes against the intended segmentation model.
Validate that configuration changes did not unintentionally expand access.
Keep an approval and evidence trail for exceptions.
The goal is not segmentation for its own sake. It is to make allowed communication deliberate and unnecessary communication harder.
Pillar 3: Build Operational Assurance
A security design is only dependable when operations preserve it. Configuration drift, failed changes, unmanaged credentials, aging equipment, and incomplete recovery procedures can all undermine an otherwise sound architecture.
Operational assurance means being able to answer basic questions quickly: What changed? Who changed it? Is the current configuration backed up? Can the previous state be restored? Does the asset have known vulnerabilities? Is it approaching end of life? Does the environment still match the intended policy?
Actionable controls
Back up network configurations and retain version history.
Review changes for drift and policy violations.
Test rollback procedures before an urgent incident.
Track vulnerabilities and end-of-life status per asset.
Protect administrative access and credentials.
Automate repeatable changes rather than relying on undocumented manual steps.
Collect evidence continuously for internal and regulatory reviews.
How ConnectMyAssets Helps
ConnectMyAssets provides an on-prem, vendor-agnostic foundation for applying this operating model across multi-vendor infrastructure.
The Dynamic CMDB and Topology modules maintain asset context and network relationships in one operational record.
Firewall Management supports the review and administration of controls governing network flows.
Backup & History provides configuration versioning and one-click rollback, helping teams investigate changes and recover a known state.
Per-asset CVE Tracking and End-of-Life Tracking connect vulnerability and lifecycle exposure to the equipment that requires action.
The Compliance Engine helps evaluate controls and retain evidence for NIS2, ISO 27001, PCI, CISA, and NIST-aligned programs.
Credential Vault and SSH Bastion strengthen the management path used to administer infrastructure.
Automation & ZTP help turn approved, repeatable procedures into consistent execution.
AI Insights, processed locally, can assist teams in interpreting infrastructure information while keeping the platform on premises.
ConnectMyAssets does not replace network architecture or security policy. It provides the inventory, history, control, and evidence needed to operate them consistently.
A Practical Adoption Sequence
Build and validate the asset inventory.
Identify critical services and map their network dependencies.
Document required flows and compare them with current policy.
Remove unjustified access paths and formalize exceptions.
Baseline configurations and enable versioned backups.
Prioritize CVE and end-of-life remediation by asset importance.
Automate recurring checks and approved changes.
Review evidence regularly to confirm that the intended security posture still exists.
The network becomes an effective security layer when design and daily operations reinforce one another. Inventory supplies context, segmentation limits exposure, flow controls enforce intent, and operational assurance keeps those protections dependable as the environment changes.
Source: Cisco