A Critical Flaw at the Network Edge
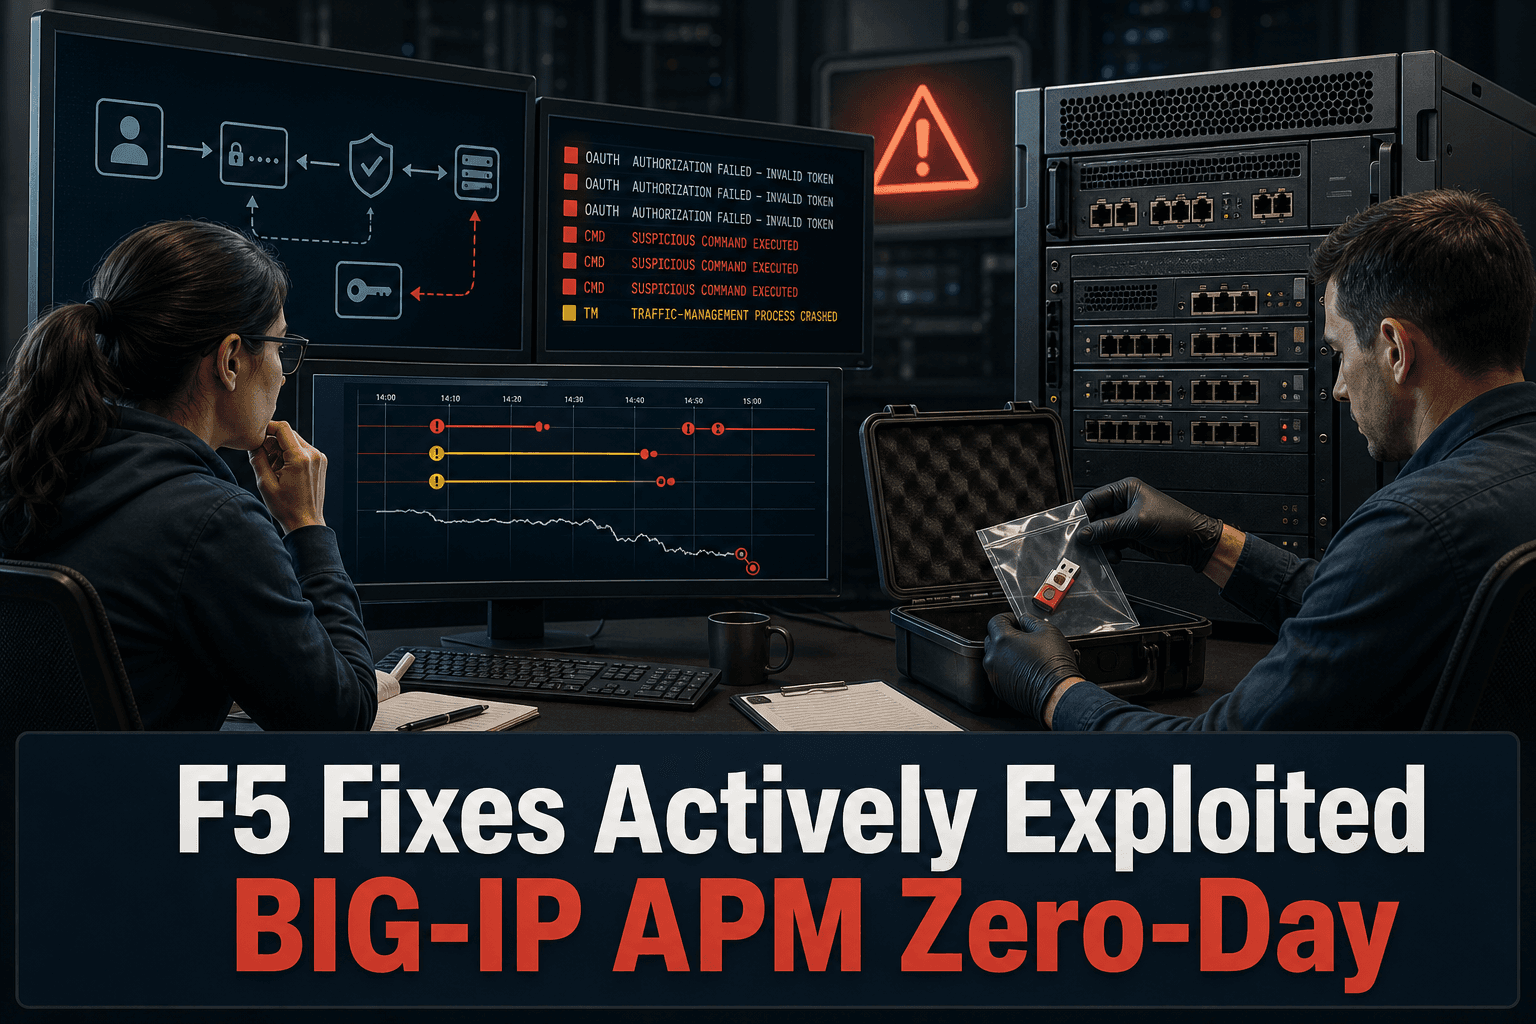
F5 has fixed CVE-2026-94127, a critical remote code execution vulnerability in BIG-IP Access Policy Manager (APM). The heap-based buffer overflow has a CVSS score of 9.8 and was being actively exploited before a patch became available.
BIG-IP APM controls access to internal resources, performs client-side checks, handles authentication and authorization, and provides VPN connectivity for remote users. Its location at the network edge makes accurate asset identification and rapid remediation especially important.
The US Cybersecurity and Infrastructure Security Agency has added the vulnerability to its Known Exploited Vulnerabilities catalog, confirming exploitation in the wild.
Which Deployments Are Affected?
The vulnerability is exploitable only when a BIG-IP system has both of the following configured:
BIG-IP APM
An OAuth authorization server profile
The issue also affects BIG-IP systems operating in appliance mode when those conditions are met. According to F5, deployments that use APM solely as an OAuth client or resource server are not affected.
That distinction makes configuration context essential. An inventory showing that APM is installed is not enough: teams must determine the OAuth role configured on each system.
The Shadowserver Foundation tracks more than 15,000 internet-exposed BIG-IP APM deployments, with roughly 5,000 located in North America and another 5,000 in Europe. These figures do not indicate how many systems have the vulnerable OAuth authorization server configuration.
Available Hotfixes and Mitigation
F5 advises customers to apply the hotfix corresponding to their supported release branch:
21.x:
Hotfix-BIGIP-21.1.0.2.0.30.22-ENG.iso17.5.x:
Hotfix-BIGIP-17.5.1.9.0.160.12-ENG.iso17.1.x:
Hotfix-BIGIP-17.1.3.5.0.41.14-ENG.iso
F5 has also released an iRule through its support portal. It can be deployed as a temporary mitigation until the relevant hotfix is applied.
For each affected appliance, the response workflow should record:
The installed BIG-IP release branch.
Whether APM and an OAuth authorization server profile are configured.
The selected hotfix or interim iRule mitigation.
The deployment time and responsible operator.
Post-change validation and retained configuration evidence.
Check for Correlated Indicators of Compromise
F5 warns that a single indicator is not necessarily evidence of exploitation. Administrators should look for a sequence involving multiple OAuth authentication failures, followed by suspicious commands and then a TMM SIGABRT event.
More than 10 repeated OAuth failure messages—particularly from the same source IP address—should prompt further investigation. Administrators can inspect the relevant counters with:
tmctl global_oauth_stat -s total_requests,total_userinfo_requests,total_failedIf the counts appear suspicious, F5 recommends reviewing activity around the relevant timestamps in:
/var/log/auditTeams should also look for TMM core files. Exploitation can cause TMM to enter a loop and crash, producing these files. The findings must be correlated rather than treated as independent proof of compromise.
A clean patch record does not replace incident review when suspicious OAuth activity or TMM crashes occurred before remediation.
How ConnectMyAssets Helps
ConnectMyAssets provides an on-prem, vendor-agnostic way to coordinate this response across mixed network infrastructure.
Dynamic CMDB: Identify inventoried BIG-IP assets, their software branches, network exposure, and operational ownership. Configuration context can help teams separate OAuth authorization server deployments from systems used only as clients or resource servers.
Per-Asset CVE Tracking: Associate CVE-2026-94127 with the relevant appliances and track remediation status asset by asset.
Backup & History: Preserve configuration versions before and after the hotfix or iRule deployment, providing a change history and rollback point.
Compliance Engine: Record remediation checks and evidence for security-control frameworks such as NIS2, ISO 27001, PCI, CISA, and NIST.
Automation: Coordinate repeatable collection and remediation tasks across affected assets while maintaining an auditable workflow.
End-of-Life Tracking: Keep software lifecycle status visible when deciding which supported release branch and hotfix path applies.
Because ConnectMyAssets runs on premises, configuration records, asset details, and remediation evidence remain within the organization's own environment. The objective is not merely to mark the CVE as closed, but to demonstrate which systems were assessed, why they were considered affected or unaffected, what changed, and how the result was verified.
Immediate Priorities
Inventory internet-facing and internal BIG-IP APM systems.
Confirm whether each system has an OAuth authorization server profile.
Apply the correct F5 hotfix, or use the published iRule as a temporary mitigation.
Review OAuth failure counts, audit logs, suspicious commands, TMM SIGABRT events, and core files together.
Preserve before-and-after configurations and remediation evidence.
Escalate systems showing correlated indicators for human incident review.
The incident is another example of attackers targeting edge devices and VPN gateways as entry points into corporate networks. Fast patching matters, but reliable configuration context and verifiable remediation records are equally necessary.
Source: Network World