

Security Has a Time Problem
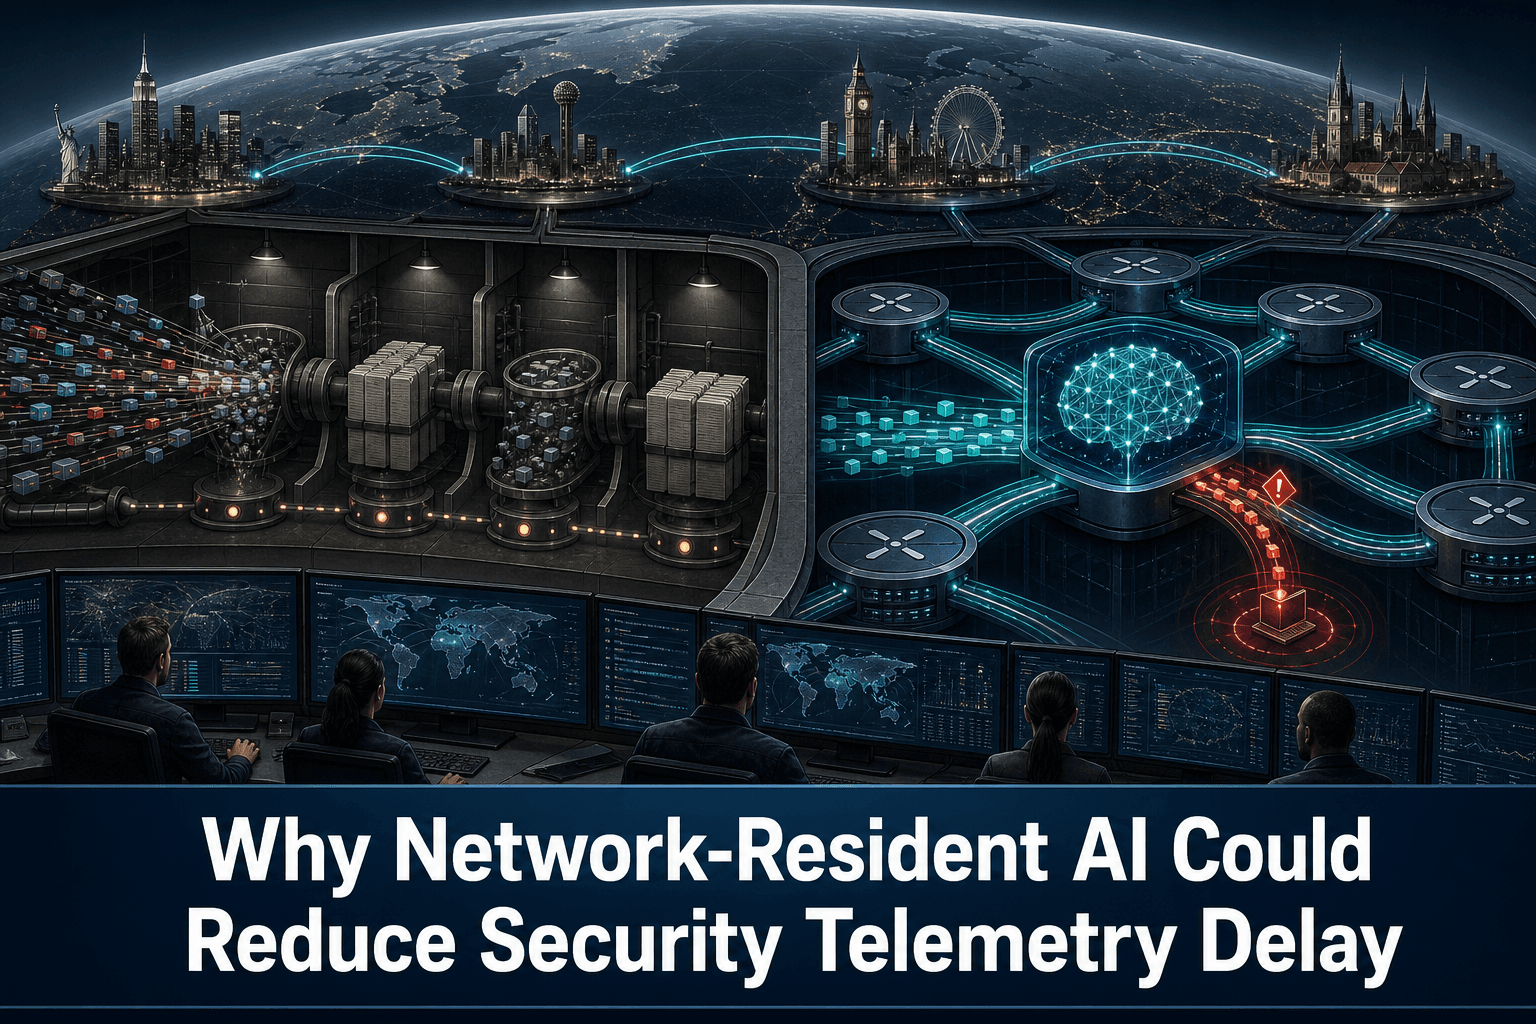
Many security systems follow a familiar sequence: collect telemetry, send it to another environment, normalize it, and then analyze it. Every stage introduces delay. As attackers use AI to identify weaknesses and develop exploits faster, that delay can extend the period during which infrastructure remains exposed.
GTT Communications is pursuing a different model with GTT Defense Halo, an AI-native network defense platform running on an AI factory embedded in the company’s global Tier 1 backbone. The infrastructure connects to New York, Dallas, London, and Prague, and each customer receives a dedicated, single-tenant instance rather than capacity in a shared cloud environment.
The underlying argument is straightforward: if valuable security data already crosses the network, analyzing it on-net may be faster than repeatedly exporting it to an external processing layer.
The strategic shift is from moving telemetry to the intelligence toward placing intelligence where the telemetry already exists.
Three Layers of Defense Halo
GTT divides the platform into three components.
Recon: Configuration and Exposure Analysis
Defense Halo Recon continuously examines firewall and device configurations. It compares them with known security frameworks to identify compliance violations and potential security exposures.
Recon also maps known CVEs to monitored customer assets and quantifies exposure risk. This connects vulnerability information with the infrastructure that may actually be affected, rather than treating every published vulnerability as equally relevant.
Detect: Customer-Specific Behavioral Baselines
Defense Halo Detect establishes a baseline of normal behavior for an individual customer’s network. It then performs continuous analysis to find anomalies beyond known CVEs and indicators of compromise.
The single-tenant model is relevant here: each environment is evaluated against its own baseline. According to GTT, this architecture also makes data residency easier to demonstrate.
Response: Approved Action Through Existing Services
Defense Halo Response passes findings through an agentic runbook into an existing security service. It can then handle approved responses across managed environments.
The word approved matters. The source describes automation tied to an established service and runbook, not an unrestricted system making arbitrary infrastructure changes.
Correlation Matters More Than Any Single Feed
GTT initially expected packet capture and software-defined networking data to provide the most valuable inputs. During development, the company instead found greater value in correlating several types of information simultaneously:
Network traffic
Identity data
Host information
User context
Syslog data
This reflects how compromises often become visible: not through one conclusive event, but through relationships among events that look less significant in isolation. A host connection, user identity, configuration state, and log entry may collectively reveal a pattern that no single tool can identify on its own.
The demonstration included a real-time “galaxy” representation of host-to-host communications. An operator could select a node, inspect its connections, and move through time to trace where an event began and how it propagated. GTT presented this as a way to reduce investigations that can take weeks to a matter of minutes, although that result still needs validation in live customer environments.
From Machine Speed to Network Speed
The security industry increasingly uses machine speed to describe the required pace of AI-assisted defense. GTT extends that idea to network speed.
Because its AI factory is embedded in its own backbone, GTT says telemetry ingestion and analysis occur on-net. This design is intended to remove egress charges and telemetry-ingestion connectivity limits while reducing the latency associated with sending data to an external platform.
The implementation combines:
Nvidia GPUs
Nvidia Morpheus, an AI application framework
Nvidia NIM inference microservices
GTT’s own patent-pending extensions
The more important architectural point is not the branding of the individual components. It is the combination of transport infrastructure and AI processing within the same network environment.
Firewall Sprawl Is the Immediate Test
The near-term use case attracting early customer interest is less futuristic than autonomous cyber defense: managing firewall policy across multiple vendors.
Enterprises with distributed sites can accumulate inconsistent rules, configuration drift, and overlapping policies. GTT is positioning real-time configuration analysis against known security frameworks—and the creation of a unified policy across vendors—as an early practical benefit.
This is also where the platform will need to prove itself. A compelling visualization and low-latency architecture are useful, but production value depends on the accuracy of findings, the quality of prioritization, and the safety of automated responses in complex customer environments.
Where ConnectMyAssets Fits
GTT Defense Halo illustrates the potential value of analyzing live traffic and correlated telemetry close to the network. ConnectMyAssets addresses the infrastructure-management side of the same operational challenge from a vendor-agnostic, on-premises platform.
Relevant ConnectMyAssets modules include:
Dynamic CMDB: Maintains an up-to-date inventory and provides the asset context needed to understand which devices are present.
Backup & History: Versions device configurations and supports one-click rollback when an approved change causes an unexpected result.
Compliance Engine: Evaluates infrastructure against NIS2, ISO 27001, PCI, CISA, and NIST requirements.
Per-Asset CVE Tracking: Associates vulnerabilities with individual managed assets, helping teams focus on exposure that is relevant to their environment.
Firewall Management: Supports multi-vendor firewall administration without forcing the organization into a single hardware ecosystem.
Automation & ZTP: Applies repeatable, controlled infrastructure changes across managed environments.
End-of-Life Tracking: Identifies assets whose support lifecycle may increase operational or security risk.
Local AI Insights: Keeps AI-assisted infrastructure analysis within the on-premises management environment.
ConnectMyAssets is not presented as a replacement for GTT’s network-resident traffic analytics, and no integration between the platforms is described in the source. Its role is complementary: maintaining reliable asset, configuration, compliance, vulnerability, and lifecycle context so infrastructure teams can validate and act on security findings with stronger operational control.
The Takeaway
GTT’s central premise is credible: defensive intelligence loses value when telemetry spends too long moving through collection and processing layers. Correlating network traffic with identity, host, user, and syslog data on-net could reduce that delay and reveal relationships hidden by siloed tools.
The remaining question is execution. Customer deployments will need to show that network-speed analysis produces accurate prioritization and safe responses—not simply faster alerts. For infrastructure teams, the broader lesson is already useful: rapid detection works best when it is paired with current asset records, controlled configurations, relevant CVE context, and reversible automation.
Source: Network World


