1. How Syslog Works in a Network
Syslog provides a standardized way for network devices to send event messages to a central collector, usually over UDP or TCP on port 514.
Each message includes:
Facility — the type of system component (e.g., kernel, daemon, auth)
Severity level — from
0 - Emergencyto7 - DebugTimestamp
Text message describing the event
Example
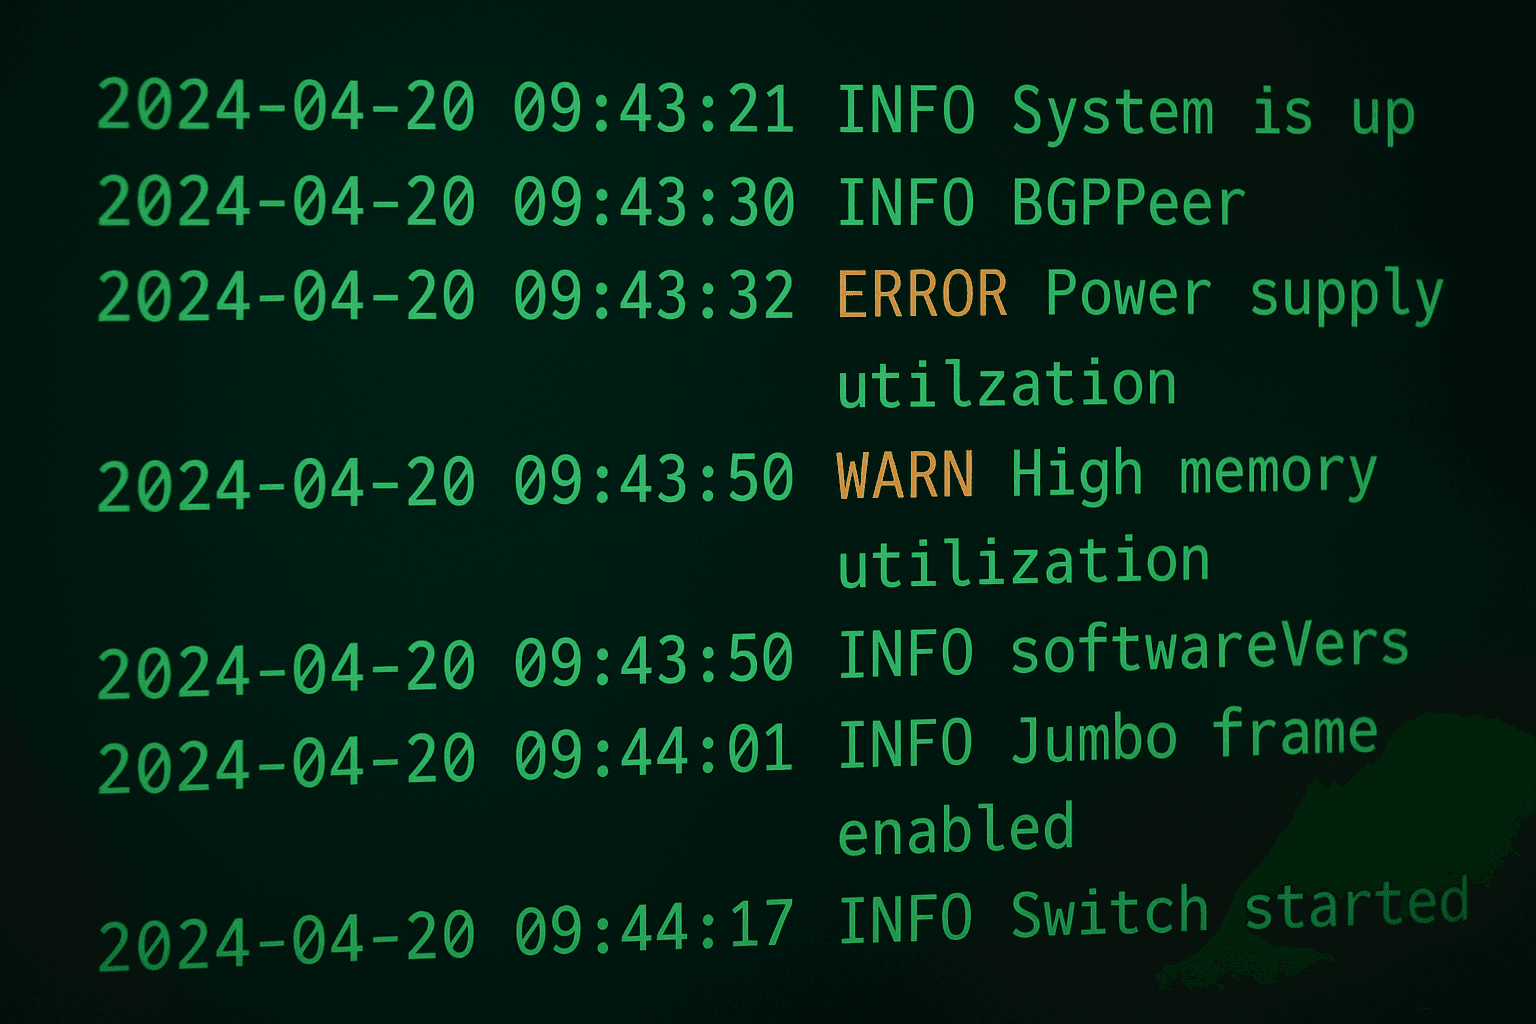
<189>Oct 06 10:15:45 core-switch %LINK-3-UPDOWN: Interface 1/1/48, changed state to down
From link state changes to authentication failures, every event can be captured and stored centrally for analysis.
2. Why Network Teams Need Centralized Syslog
Troubleshooting and Root Cause Analysis
When a connectivity issue occurs, engineers can correlate events across multiple devices in seconds.
Instead of logging into every switch, a single query in a platform like Graylog or Splunk provides a full picture — which interfaces went down, what routing updates occurred, or who made configuration changes.
Historical Insight
Centralized logging ensures that even if a device reboots or clears its buffer, the event history remains intact.
This long-term visibility is key for root cause analysis and post-incident investigations.
Multi-Vendor Correlation
Syslog creates a common event language across mixed infrastructures — Cisco, Aruba, Fortinet, Juniper, Palo Alto — enabling unified dashboards and consistent alerting logic.
3. Syslog as a Security Tool
Syslog is not only operational — it’s strategic for cybersecurity.
Network devices often provide the first indicators of compromise: failed logins, ACL hits, unexpected reboots, or configuration changes.
Centralized Syslog allows you to:
Detect suspicious or unauthorized actions in real time
Create alerts for specific log patterns (e.g., multiple failed SSH attempts)
Preserve tamper-proof logs for audit and compliance
Platforms like Splunk Enterprise Security and Graylog Security can automatically parse Syslog events, enrich them with metadata, and feed them into detection pipelines for SIEM-level analysis.
References:
4. Best Practices for Network Engineers
Use TCP or TLS for reliability and integrity. UDP is fast but can drop packets.
Define severity filters. Limit debug messages in production to avoid overload.
Tag sources properly. Ensure hostnames and device IDs are unique and meaningful.
Synchronize time (NTP). Accurate timestamps are essential for event correlation.
Monitor your Syslog flow. Configure alerts for devices that stop sending logs.
5. Conclusion
A properly configured Syslog setup is one of the simplest yet most powerful tools in a network engineer’s arsenal.
It turns your infrastructure into a talkative, observable system — one where every interface change, authentication attempt, and configuration update is captured, searchable, and actionable.
Whether you use Graylog for open-source flexibility or Splunk for enterprise-grade analytics, Syslog is the foundation of network visibility and resilience.
Without logs, your network is silent.
With Syslog, it speaks — and tells you everything you need to know.