NIS2 for Network Operators: Requirements, Reporting & Penalties
NIS2 (Directive (EU) 2022/2555) replaces the original NIS regime and raises the bar for cybersecurity across the EU. For network operators, it translates into concrete obligations: governance, technical controls, supply-chain risk, and strict incident reporting.
Who Is in Scope?
NIS2 applies to Essential and Important entities across many sectors (e.g., energy, transport, digital infrastructure, ICT service management/MSP/MSSP, health, water, public administration). Scope is set at EU level; detailed application is completed by each Member State’s transposition law. See Annexes I & II of the Directive for the full list.
What You Must Implement (Article 21 — Risk-Management Measures)
Operators must deploy appropriate and proportionate technical, operational and organisational controls, including (non-exhaustive):
Policies for risk analysis and information-system security
Incident handling and business continuity (incl. backup/disaster recovery)
Supply-chain security (suppliers, MSP/MSSP, cloud/ICT products)
Secure acquisition, development & maintenance (vulnerability handling & disclosure)
Continuous effectiveness assessment of controls
Cyber hygiene & training for staff
Cryptography (incl. encryption) where appropriate
Access control / identity & MFA, network security, and asset management
The Directive expects evidence: policies, procedures, records (tests, audits), and proof of effective operation.
Incident Reporting (Article 23)
Reporting is staged for “significant incidents”:
Early warning within 24 hours of awareness
Incident notification within 72 hours (initial assessment + severity/impact + IoCs if available)
Final report within one month (root cause, impact, mitigations; progress report if still ongoing)
Your CSIRT/competent authority provides initial feedback (ideally within 24h). Keep runbooks and templates ready.
Penalties (Article 34)
Administrative fines can reach:
Essential entities: up to €10M or 2% of worldwide annual turnover (whichever is higher)
Important entities: up to €7M or 1.4% of worldwide annual turnover
Supervision also includes corrective orders, audits and inspections.
Timeline & Enforcement
Transposition deadline: 17 Oct 2024; measures apply from 18 Oct 2024 at national level.
Compliance is ultimately checked against your Member State’s transposition and any implementing acts/guidance. Validate local thresholds and sector specifics.
Practical Playbook for Network Teams
1) Governance & Evidence
Map responsibility to management; maintain policies (risk, changes, backups, incident response).
Centralise evidence: configs, backup logs, restoration tests, change approvals, incident reports.
2) Configuration & Change Management
Enforce standard baselines; backup configs after each change; version and diff.
Quarterly restoration drills; document RTO/RPO.
3) Monitoring & Detection
Centralise logs (Syslog/TLS), flows, and admin actions; define “significant incident” triggers.
Maintain CSIRT notification templates (24h/72h/1-month).
4) Vulnerability & Patch
Track advisories; define SLA by criticality; record exceptions/mitigations.
5) Access & Network Security
MFA for admin access, least privilege, jump hosts, network segmentation, encrypted management planes.
6) Supply-Chain
Security clauses in contracts (vuln handling, SBOM/patch SLAs, incident cooperation), vendor assurance records.
How ConnectMyAssets Helps (On-Premise Only)
ConnectMyAssets runs entirely inside your environment (no cloud dependency). It helps produce audit-ready evidence for NIS2 across multi-vendor networks:
Automated configuration backup & versioning (on-change & scheduled), local encrypted storage
Drift & diff across devices; restore assistance with pre-deployment checks
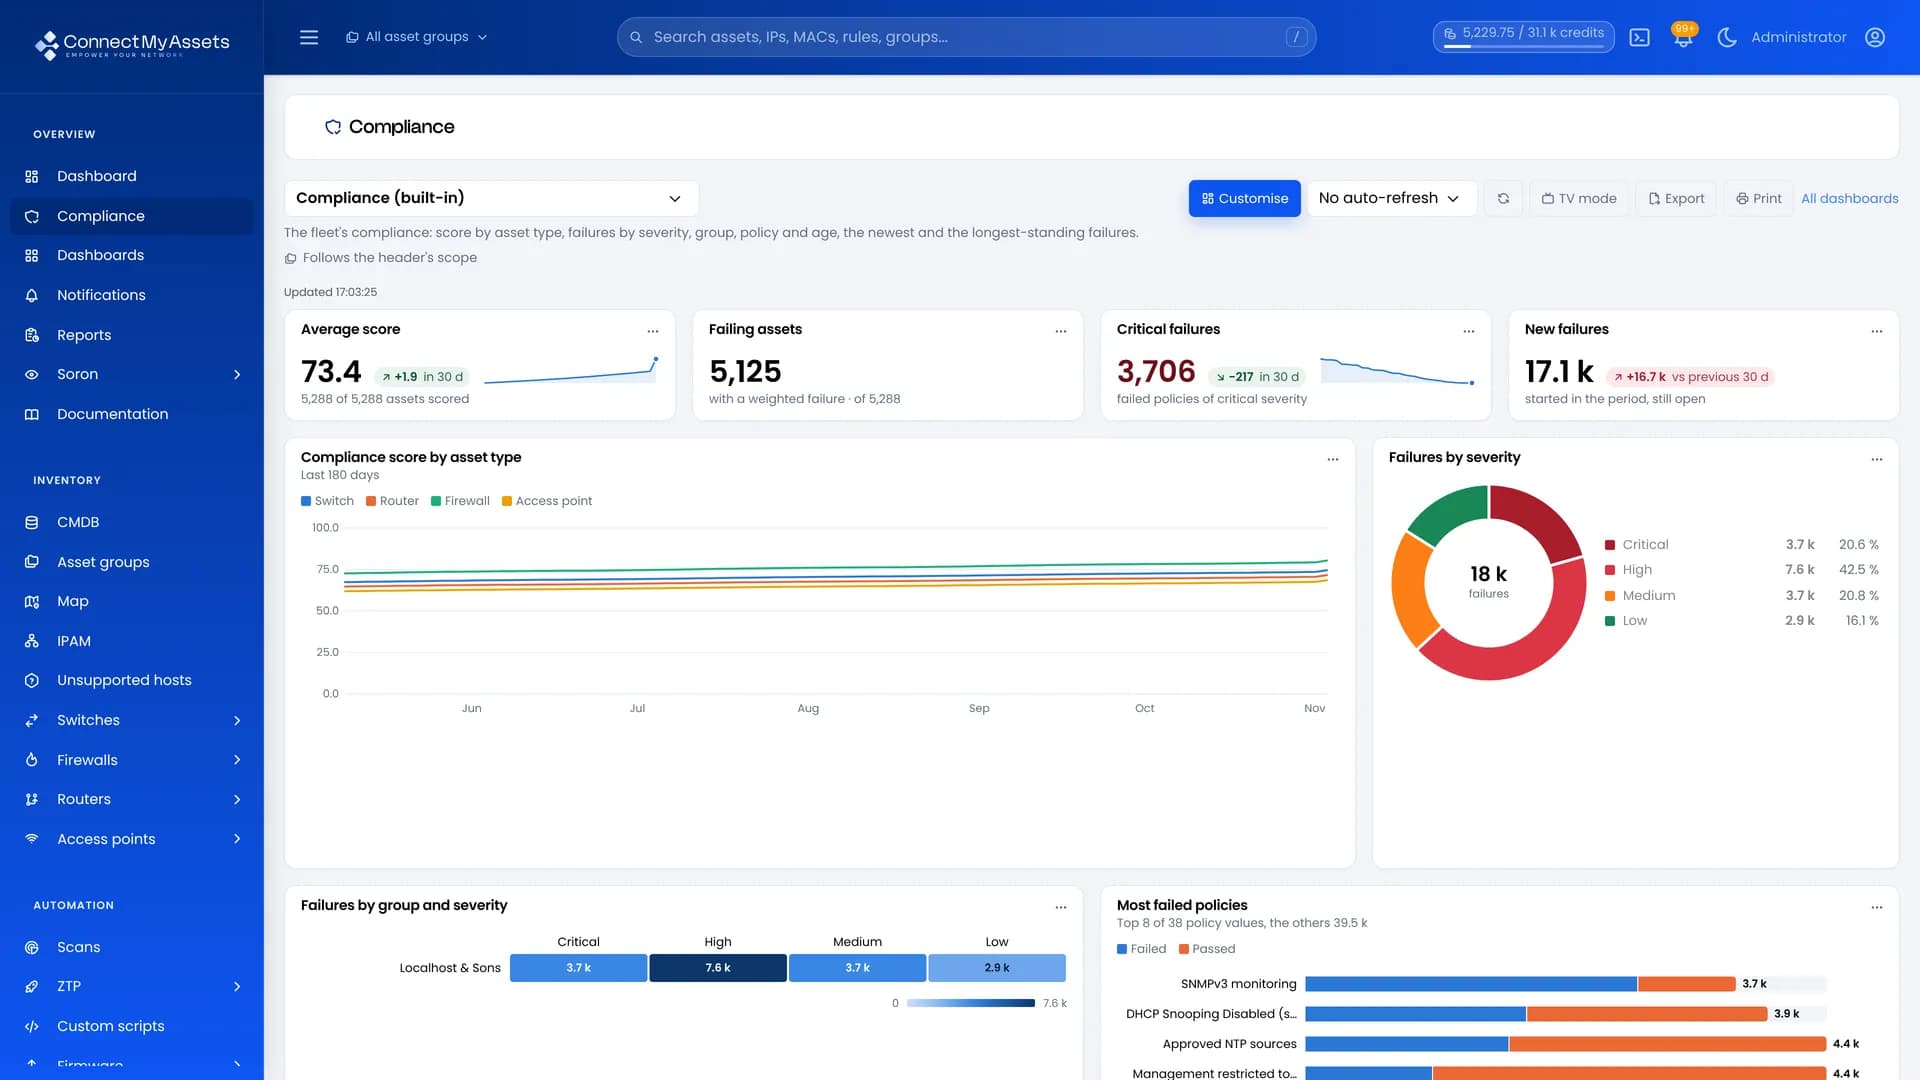
Baseline & compliance checks mapped to NIS2 control areas (config hygiene, access, logging, backups)
Full audit trails & reports exportables for inspections (management accountability, Art.20/21)
Result: consistent controls, faster incident investigations, and clear evidence for regulators — with all data staying within your perimeter.
References (official sources)
EUR-Lex — NIS2 full text (HTML): https://eur-lex.europa.eu/eli/dir/2022/2555/oj/eng
EUR-Lex — NIS2 PDF (Official Journal): https://eur-lex.europa.eu/legal-content/EN/TXT/PDF/?uri=CELEX:32022L2555
ENISA — NIS2 Technical Implementation Guidance (2025): https://www.enisa.europa.eu/publications/nis2-technical-implementation-guidance